


Your Connection Is Not Private: What It Means and How to Fix It
-
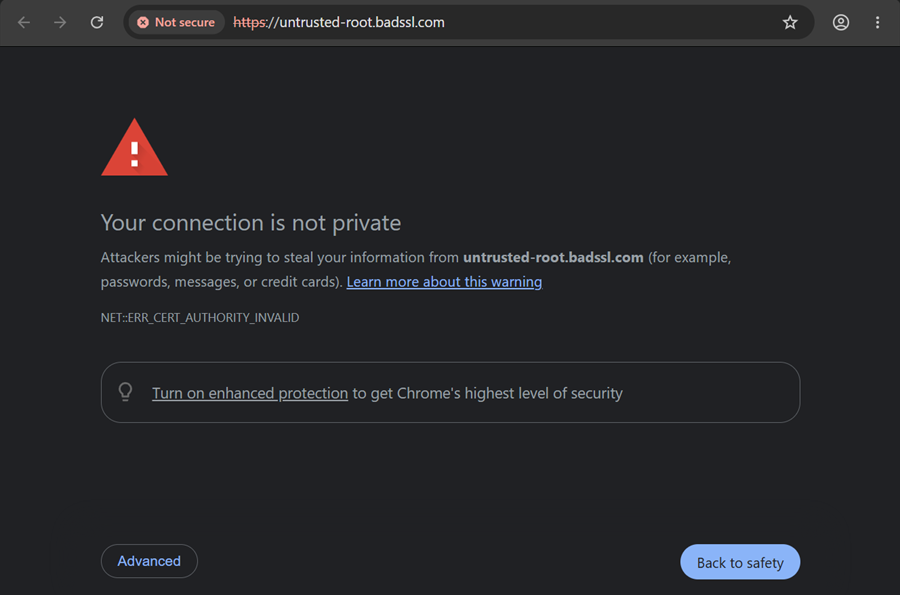
"Your connection is not private" is the warning Chrome shows when it cannot verify a website's SSL certificate. Edge says "Your connection isn't private", Firefox "Warning: Potential Security Risk Ahead" and Safari "This Connection Is Not Private". The warning itself is only the headline: the error code under it tells you what went wrong and who has to fix it. This guide shows how to find the code, what each code means and what to do as a visitor or as a website owner.
- Automatic renewals
- Less manual work
-
-
1
What the warning means
Before a browser opens an HTTPS page, it checks the website's certificate. Three checks matter most:
- Trusted issuer. The certificate must lead, through its intermediate certificate, to a certificate authority (CA) the browser trusts.
- Right name. The certificate must cover the exact address you opened, for example both example.com and www.example.com.
- Valid dates. The certificate must not be expired, and your device's clock must be correct.
If any check fails, the browser stops and shows the warning instead of the page. It does not always mean an attack: most of the time the certificate is expired, incomplete or installed for the wrong name, or something on your own device gets in the way. But the browser cannot tell these cases apart from an attacker sitting between you and the website, so treat the warning seriously.
-
2
Find the error code
- Chrome and Edge show the code under the message, for example NET::ERR_CERT_DATE_INVALID. Click it to see the certificate details.
- Firefox shows the code after you click "Advanced…", for example SEC_ERROR_UNKNOWN_ISSUER.
- Safari shows the reason after you click "Show Details".
Then look the code up in the table and open the matching guide:
Error code What it means NET::ERR_CERT_AUTHORITY_INVALID
Firefox: SEC_ERROR_UNKNOWN_ISSUERThe certificate does not lead to a trusted CA: it is self-signed, the intermediate certificate is missing, or antivirus or a proxy intercepts the connection. NET::ERR_CERT_COMMON_NAME_INVALID
Firefox: SSL_ERROR_BAD_CERT_DOMAINThe certificate was issued for a different name, for example only for www.example.com while you opened example.com. NET::ERR_CERT_DATE_INVALID
Firefox: SEC_ERROR_EXPIRED_CERTIFICATEThe certificate has expired or is not valid yet, or the clock on your device is wrong. NET::ERR_CERT_REVOKED
Firefox: SEC_ERROR_REVOKED_CERTIFICATEThe CA has cancelled the certificate, for example because its private key leaked. Only the website owner can fix it, by installing a new certificate. NET::ERR_CERTIFICATE_TRANSPARENCY_REQUIRED The certificate was not published in public Certificate Transparency logs, which Chrome requires. NET::ERR_SSL_PINNED_KEY_NOT_IN_CERT_CHAIN The website's key does not match the key the browser expects for it (key pinning). Some errors look similar but come with a different headline. "This site can't provide a secure connection" means the secure connection could not be set up at all: see ERR_SSL_PROTOCOL_ERROR and ERR_SSL_VERSION_OR_CIPHER_MISMATCH. Firefox's "Secure Connection Failed" with SSL_ERROR_RX_RECORD_TOO_LONG usually means the server answers HTTPS requests without SSL. A "Not secure" label in the address bar without a warning page is a different issue: see Why no padlock.
-
3
Solutions for website visitors
First open the same website on another device that uses a different network, for example your phone on mobile data. If the warning appears there too, the website's certificate is at fault and only its owner can fix it. If the website opens fine elsewhere, the cause is on your computer or network:
- Reload the page and check the address. A typo or an old bookmark can lead to a name the certificate does not cover.
- Check the date and time. Turn on automatic date, time and time zone in your system settings, then restart the browser.
- Leave public or hotel Wi-Fi. Many public networks redirect you to a login page first. Open any website without HTTPS to bring up the login page, or switch to mobile data.
- Check your antivirus or firewall. Features called "HTTPS scanning", "web shield" or "SSL inspection" replace the website's certificate with their own. Turn the feature off for a moment, or update the antivirus, and reload the page.
- Turn off VPN, proxy and browser extensions. Test in an Incognito window with extensions disabled.
- Update your operating system and browser. Old systems lack newer root certificates and no longer trust many websites.
You can click "Advanced" → "Proceed to … (unsafe)" to open the page anyway, but never do this on sites where you log in, pay or enter personal data. On websites that use HSTS, Chrome does not offer this option at all. On a company computer, ask your IT team before you bypass the warning: a missing corporate root certificate is a common cause there.
-
4
Solutions for website owners
If visitors report the warning, test your site with our free SSL Checker. It shows the certificate's names, dates and chain. Then work through the usual causes:
- Renew an expired certificate and install the new one on every server that serves the site.
- Install the intermediate certificate. Without the full chain, some browsers and phones cannot reach a trusted root. Download the bundle from our intermediate and root certificates pages.
- Cover every name. The certificate must include each address visitors use, with and without www. For many subdomains use a Wildcard SSL, for several different domains a Multi-Domain SSL certificate.
- Replace self-signed and test certificates. Public visitors always see the warning for them. A trusted domain-validated certificate such as Sectigo PositiveSSL costs from $16.00 per year and is issued in minutes.
- Serve the right certificate. When several sites share one server, a missing virtual host can serve the default certificate of another site. Check the server configuration for each domain.
Most of these problems come from manual renewals. Automated SSL issues, installs and renews certificates for you, with the correct intermediate chain.
-
Your connection is not private: frequently asked questions
What does "Your connection is not private" mean?
The browser could not verify the website's SSL certificate, so it cannot be sure that it is talking to the real website. The error code under the message tells you why.
Is it safe to continue to the website?
Only if you know why the warning appears, for example on your own test server. Never continue on a site where you log in, pay or enter personal data, because the same warning appears when someone intercepts the connection.
Does the warning mean I have been hacked?
Usually not. Most warnings come from an expired or wrongly installed certificate, a wrong system clock or security software on your device. If the warning appears on many well-known websites at once, check your network, antivirus and proxy settings.
Why do I see it on every website?
Then the cause is on your device or network: a wrong system clock, antivirus HTTPS scanning, a proxy or VPN, a public Wi-Fi login page or an outdated operating system.
How do I fix the warning on my own website?
Test the site with an SSL checker, then renew an expired certificate, install the intermediate certificate, make sure the certificate covers every name of the site and replace self-signed certificates with one from a trusted CA.
